How to Check If an Email Address Has Been Used Online
Learn how to check if an email address has been used online and find associated accounts with email OSINT search.
Checking whether an email address has been used online is useful in two situations: auditing your own exposure, and judging whether an address someone gave you belongs to a real, established person. The checks are the same in both cases. What changes is how carefully you treat the results, and how much weight you put on a silent result.
Short version: an address leaves traces in four places (public pages, sign-up forms, breach records, and linked identifiers). Search all four, write down where each hit came from, and never treat an empty result as proof that nothing exists.
What “Online Presence” Actually Means for an Email Address
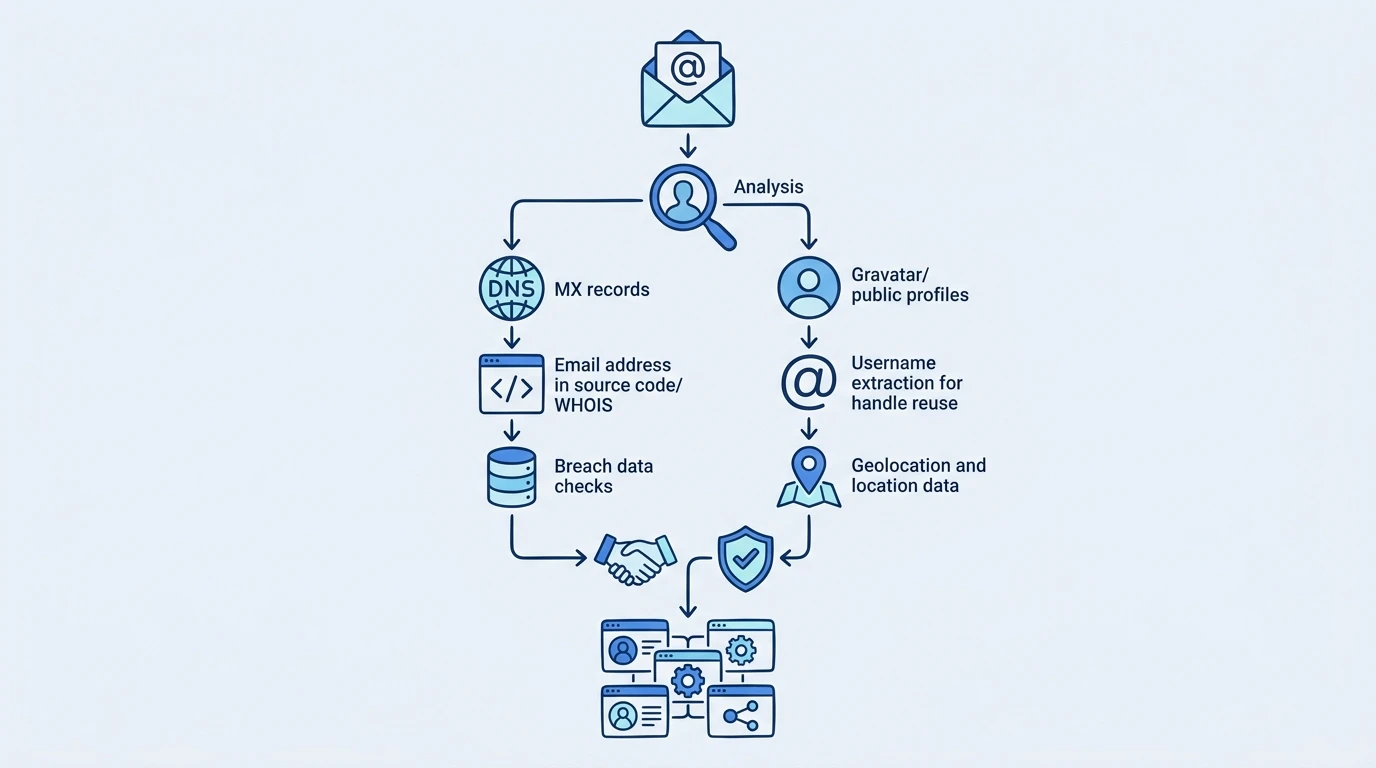
An email’s online presence is made up of four kinds of traces, and each one is found with a different method:
- Public mentions: the address written on web pages, forum posts, documents, or code repositories.
- Registered services: websites where an account exists for the address, even if you forgot about it years ago.
- Breach records: appearances in known data breaches, which reveal services that used to hold the address.
- Linked identifiers: usernames, names, or phone numbers that appear next to the address in public sources.
Email footprint checkers look at some or all of these. No single tool sees everything, so combining methods gives the most complete answer. If you want the manual search techniques in more depth, our guide on finding websites associated with an email address walks through them one by one.
The Numbers Behind Email Exposure
Before the practical steps, it helps to see how big the problem is. Have I Been Pwned (HIBP), the breach notification service run by security researcher Troy Hunt, publishes the list of every breach it has loaded through a public endpoint. We pulled it on November 7, 2026 and counted.
The 17.85 billion figure is a sum of records, not of people. The same address often appears in many breaches, so it says more about how much data is circulating than about how many individuals are affected. The useful number for an email check is the next one: 1,042 of the 1,049 breaches (99.3%) contain email addresses. If an address has been used on the internet for a few years, the odds that it sits in at least one of these datasets are far from small.
Chart 1: What data do breaches contain?
An email address on its own is a weak identifier. What makes a breach record valuable to an investigator, and dangerous to the owner, is what sits next to it:
/api/v3/breaches endpoint on November 7, 2026. A breach can contain several types, so the bars do not add up to 100%. Source: haveibeenpwned.com/API/v3.Two lines stand out. First, passwords appear in 674 breaches, roughly two out of three, which is why password reuse is the single habit that turns an old breach into a present-day account takeover. Second, usernames show up in 485 breaches (46.2%). That is the link between an email lookup and a username search: a breach entry can hand you a handle you would never have guessed from the address.
Chart 2: Is it getting better?
You might hope the trend is downward. The data does not really say so:
BreachDate field), not the year it was added. Recent years can still grow as older incidents come to light. Data retrieved November 7, 2026. Source: haveibeenpwned.com/API/v3.The count moves around rather than falling. 2016 was the busiest year in the index with 104 breaches, 2023 was a quiet one with 47, and 2026 already has 91 with a few weeks still to go. Two cautions apply. A breach is often loaded months or years after it happened, so the most recent bars are likely to grow. And the index only contains breaches that were found and verified, so it is a floor, not a ceiling.
The Biggest Breaches in the Index
A handful of enormous datasets account for a large share of the total. These are the eight largest by number of records, again from the November 7, 2026 pull:
| Breach | Breach date | Records |
|---|---|---|
| Synthient Credential Stuffing Threat Data | 2025-04-11 | 1,957,476,021 |
| Collection #1 | 2019-01-07 | 772,904,991 |
| Verifications.io | 2019-02-25 | 763,117,241 |
| Onliner Spambot | 2017-08-28 | 711,477,622 |
| Data Enrichment Exposure From PDL Customer | 2019-10-16 | 622,161,052 |
| Exploit.In | 2016-10-13 | 593,427,119 |
| 2019-08-01 | 509,458,528 | |
| Anti Public Combo List | 2016-12-16 | 457,962,538 |
Notice that several of these are not breaches of a single company. Collection #1, the Anti Public Combo List and the credential stuffing dataset are compilations of earlier leaks, and Verifications.io was an email verification service that exposed other people’s lists. That matters for interpretation: finding your address in one of them tells you it was circulating, not necessarily which website you originally signed up on.
A Five-Step Check
Here is the order we would work in. It goes from the quietest, lowest-risk checks to the ones that touch third-party services.
- Search the exact address. Put it in quotes, for example
"[email protected]", in more than one search engine. Addsite:github.comorfiletype:pdfto target code and documents, and try obfuscated forms such as “name at example dot com”. - Check breach exposure. Look the address up in a breach notification service such as Have I Been Pwned. Breach entries show which services held the address, even if the accounts were later deleted. For your own address, you can also ask HIBP to notify you of future breaches.
- Run registration checks. Use an email OSINT tool such as Holehe OSINT to test which sites recognize the address. The next section explains what these checks do and do not prove.
- Test the username. Search the part before the
@as a username, and verify any matching profiles before connecting them to the email. - Write down what you found. Record each result with its source and date, and mark which ones are confirmed and which are only possible.
How Registration Checks Work
Step three deserves a closer look, because it is the part people misunderstand. A registration check does not read anyone’s account. It sends the address to a site’s public sign-up, login or password-recovery form and looks at how the response differs when the address is already known. “That email is already registered” is a different reply from “check your inbox to confirm”.
The open-source Holehe project is a good illustration because its README lists every module in a table. We counted that table on November 7, 2026:
Four out of five modules use the sign-up form, which is the form most likely to say “this address is taken”. The table also marks 31 of the 121 modules (25.6%) as frequently rate limited, so a quarter of the checks can return an error rather than an answer on a busy day. That is why a result list contains an error state as well as found and not found, and why a rate-limited line should be re-run later rather than read as a negative. For a wider comparison of what other tools cover, see Holehe vs Sherlock vs Maigret vs WhatsMyName.
One more limit worth stating plainly: the table is a snapshot of one project. Sites change their forms, and large platforms increasingly give the same reply for known and unknown addresses precisely so that this kind of check does not work. Treat a hit as a lead and a miss as “unknown”.
Video: Where Breach Data Comes From
If you want the story behind the breach lookup in step two, this conference talk by Troy Hunt explains how Have I Been Pwned collects breach data, why he built it, and what people typically do wrong after finding out they are in it. It runs about fifty minutes, so it is one for later rather than for a quick check.
Video: “Have I Been Pwned? • Troy Hunt • GOTO 2023” by GOTO Conferences on YouTube, shown for educational purposes and not affiliated with this site.
Signs an Email Address Has Been Used Online
- A registration check confirms the address on one or more platforms
- Search engines return profile pages, forum posts, or documents mentioning the exact address
- The address appears in one or more public breach records
- The address is the commit author on public code repositories
- A profile photo or display name linked to the address appears consistently across services
The opposite pattern matters too. A brand-new address with no mentions, no registrations, and no breach history is not proof of anything, but in fraud review it can be a reason to ask for extra verification. A supplier contact whose “ten-year-old” company address has never appeared anywhere is worth a second look.
Which Method Answers Which Question
The five methods overlap less than they seem to. Use this table to pick the one that fits the question you are actually asking:
| Question | Best method | What it cannot tell you |
|---|---|---|
| Is this address published anywhere? | Exact-match web search | Anything on pages search engines have not indexed |
| Has it been in a known leak? | Breach notification service | Leaks that were never found or loaded |
| Does a site have an account for it? | Registration check | Who owns the account, or whether it is active |
| Is the same person behind other handles? | Username search | Whether a matching handle is the same human |
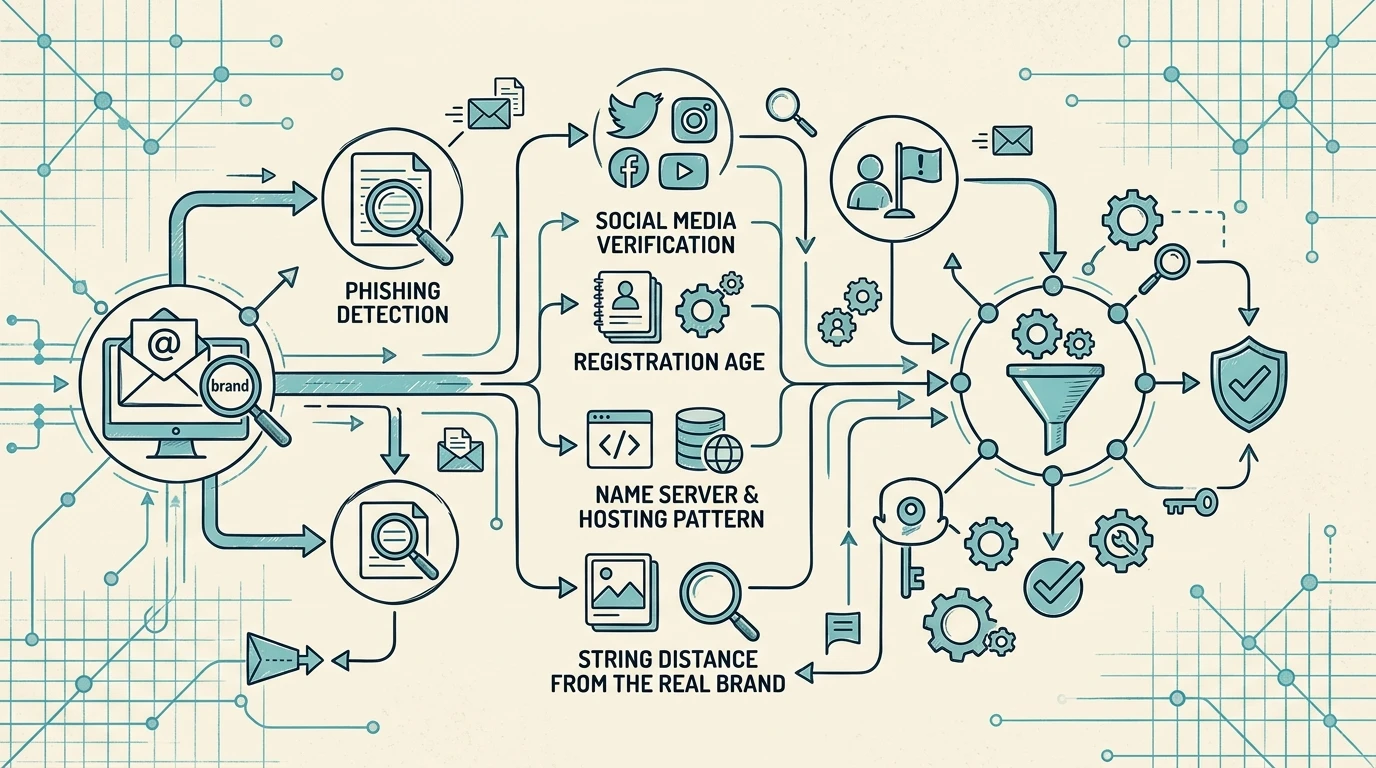
| Is it a throwaway address? | Domain and pattern review | Intent: plenty of real people use disposable addresses |
What the Results Do Not Tell You
- Who controls the account. A registration only shows the address was used to sign up.
- Whether an account is still active. Many accounts are abandoned but never deleted.
- Anything private. Legitimate OSINT tools do not reveal messages, passwords, or private profile data.
- Whether you were personally targeted. A breach entry means the data was exposed to someone, not that anyone used it.
Avoid testing someone else’s address by starting a password reset; the owner may be notified, and it can breach platform terms. For the same reason, stick to your own addresses or work you are authorised to do. The broader picture of how these signals combine is covered in Top OSINT Techniques for Digital Footprint Investigation.
What to Do If You Find Unexpected Accounts
If a check on your own address reveals accounts you do not recognize, act in this order:
- Secure the email account first: change its password and turn on two-factor authentication, because whoever controls your inbox can reset everything else.
- Review the email account’s connected apps and forwarding rules, and remove anything you did not set up.
- Visit each unexpected service, use “forgot password” to regain access, then delete the account or secure it.
- Change any password that was reused on a breached service. This is where the 674 password-bearing breaches in Chart 1 become personal.
- Switch to a password manager so every account has its own password. NIST’s digital identity guidelines (SP 800-63B) go further and recommend that services compare new passwords against lists of known-compromised ones, which is exactly what makes reuse so risky.
Repeating this audit once or twice a year is one of the simplest ways to reduce exposure to account takeover and phishing. If you are also curious about the other identifiers that can be linked to you, the phone number OSINT guide covers the same questions for a number, and how we protect search privacy explains how searches on this site are handled.
Frequently Asked Questions
Can I check if an email has been used online without installing anything?
Yes. An exact-match web search, a breach lookup on Have I Been Pwned, and a browser-based email OSINT tool all run in a normal browser. Installing a command-line tool only becomes worthwhile if you plan to run many checks.
Does finding my email in a breach mean my account was hacked?
Not by itself. It means the data was exposed. Whether anyone used it depends on whether the password was also exposed (it was in 674 of the 1,049 indexed breaches) and whether you reused it elsewhere. Change the password and turn on two-factor authentication to close the risk.
Why does a tool say “not found” when I know I have an account?
The site may hide the difference between known and unknown addresses, the check may have been rate limited, or the module may be out of date because the site changed its form. A “not found” result is never proof that no account exists.
Is checking someone else’s email address legal?
The checks described here use public pages and public sign-up responses, but the legal position depends on your country and on what you do with the result. Stick to your own addresses or work you are authorised to do, and keep a record of why.
How often should I run this check on my own address?
Once or twice a year is a sensible rhythm, plus whenever a service you use announces a breach. Signing up for breach notifications on your own address covers the gaps in between.
Sources and Further Reading
- Have I Been Pwned API v3 documentation: the breach index used for every figure in Charts 1 and 2
- Holehe on GitHub: the module table used for Chart 3
- NIST SP 800-63B, Digital Identity Guidelines: Authentication and Lifecycle Management: guidance on screening passwords against breached lists
- Have I Been Pwned? Troy Hunt, GOTO 2023: the video embedded above
Figures in this article were retrieved from the sources above on November 7, 2026. Breach counts change as new incidents are loaded, so check the source for the current number.